Last updated: November 3, 2026
By Kris Drouet, Engineering Executive, in partnership with KORE1
Before a remote contract engineer gets repository credentials, verify identity on live video with camera controls, match the ID to the person on screen, ship the laptop only to the ID address, and call references you found yourself. Then tie that verified person to their git identity with a hardware key and signed commits. Okta tied North Korean IT-worker operatives to more than 6,500 job interviews at over 5,000 companies through mid-2025.
Every control in my repo rests on one sentence. The account belongs to the person we interviewed.
MFA assumes it. Branch protection assumes it. Code review assumes the reviewer knows who wrote the diff, and the audit log assumes the name on each line is a person you could pick out of a lineup. None of those controls checks the sentence. They inherit it.
That used to be a safe inheritance. Is it still?
I don’t think so, and I’ve stopped treating contractor identity verification as an HR form that finishes before engineering gets involved. It’s an access control. Plain and simple. It belongs to whoever owns the repo, which in most regulated shops I’ve worked in means you. If you’re bringing engineers in through contract staffing, this piece is about the checks I want done before the first credential goes out, how to bind the verified human to the commits, and what to watch for once they’re in.
A note on where I sit. I write in partnership with KORE1, which places contract engineers. There’s a box near the end in KORE1’s own voice. Judge it like any vendor’s claims. I would.
How Big Is the Fake-Identity Problem?
Big enough that I stopped calling it a fringe risk. Show me the data, and here it is, all from primary sources.
| Source | Date | What it found | Why an engineering leader should care |
|---|---|---|---|
| Okta Threat Intelligence | Sept. 30, 2025 | More than 130 identities tied to more than 6,500 initial job interviews at over 5,000 companies through mid-2025 | Remote software development roles were the most targeted positions |
| FBI PSA I-012325-PSA | Jan. 23, 2025 | Workers used AI and face-swapping in video interviews, copied company repositories to personal accounts, and held code for ransom | The target is your source code, not just a paycheck |
| FBI PSA I-072325-4-PSA | July 23, 2025 | U.S.-based facilitators receive and reship company laptops, and contract IT work is a common way in | Contract seats are named as the entry point |
| U.S. Department of Justice | June 30, 2025 | 21 premises searched in 14 states from June 10 to 17, about 137 laptops seized, jobs at more than 100 U.S. companies | Workers got access to sensitive employer data and source code |
| KnowBe4 | July 23, 2024 | A hire passed four video interviews and a clear background check on a stolen U.S. identity | A security company’s hiring process still let the person through |
Two numbers in Okta’s report get less attention than the headline. Okta found that at most 10% of those candidates progressed to follow-up interviews, and that 73% of the targeted roles were advertised by U.S.-based firms. So the volume is huge and the hit rate is low. That’s a numbers game. Volume wins those. Somebody’s screen is going to be the one that misses.
The FBI’s January 2025 advisory is the one I’d forward to your staff engineers, because it isn’t about payroll fraud at all. In PSA I-012325-PSA, the Bureau says North Korean IT workers have copied company code repositories, such as GitHub, to their own user profiles and personal cloud accounts, held proprietary code hostage for ransom, and in some cases released it publicly. Read that twice if you run a repo. Then check your fork settings.
The Justice Department’s June 2025 action adds the physical side. Laptop farms. Rooms full of company laptops, each one logged in for somebody else. The same release describes one case in which a co-conspirator got into a California defense contractor’s laptop and took export-controlled data covered by ITAR.
Why Are Remote Contract Engineers the Easiest Door?
Because we built the door to open fast. On purpose. I say that as someone who has asked for exactly that. Repeatedly.
The FBI’s July 2025 advisory is blunt about it. “Contract IT work is a common way that North Korean IT workers procure employment,” PSA I-072325-4-PSA says, and it describes facilitators setting up U.S. front businesses that claim to offer short-term technical contract workers.
Think about what a contract start looks like from the inside. One or two interviews, often fewer than a full-time loop. A hiring manager who assumes the agency did identity. An agency that assumes the client will do it at onboarding. A laptop shipped to whatever address is on the form. Often nobody checks it. Repository access inside the first week, because the whole reason you bought the seat was to skip the ramp. Across KORE1’s contract placements the median offer-to-start is 3 days (n=1,997), so there isn’t much calendar for anyone to notice a problem.
Each handoff is reasonable on its own. Together they leave a gap where nobody owns the question “is this the person?”
Speed is fine. Nobody owning it is the problem.
What Should You Require Before Credentials Issue?
Here’s my short list. I want every item done, by a named person, before a contractor’s account can authenticate to anything with source code behind it.
- A live video interview with the camera on, an unobscured background, and the candidate showing the room around them. The FBI’s July guidance also suggests asking the person to wave a hand in front of their face.
- Take a photo at that interview. Compare it at later meetings. The FBI recommends this because someone else may do the work after a different person passes the interviews.
- Government ID matched against the face on screen, then against the name on payroll and the bank account. Mismatches here are the cheapest catch you will ever make.
- The laptop ships only to the address on the ID. Any other address needs more documents, per the FBI. KnowBe4 flagged a shipping address that doesn’t match where someone claims to live as a red flag in its own write-up.
- References you found yourself. Not the phone numbers on the resume. Call the company switchboard and ask for the person by name, the way Okta recommends.
- No system access until the background check is complete. That’s an FBI recommendation, not my preference, though it is also my preference.
Six items. No vendor required. Nothing exotic.
A clean background check isn’t on the list as proof of anything, and the KnowBe4 case is why. KnowBe4 hired a principal software engineer who passed four video interviews, and the check came back clear because the identity checked out. The person didn’t. Clean record, wrong person. The photo had been AI-enhanced from a stock image. A background check tells you an identity exists and is clean. It can’t tell you who is sitting in the chair. What a check legally covers is a separate topic, and the background check guide for employers handles it.
If you run the interviews yourself, the tells on camera are covered well in how to spot a face swap or proxy in a remote interview, and the skills side is in how to interview contract engineers. I won’t repeat either here. Different problem. My concern starts where theirs ends, at the moment a verified person becomes an account.
How Do You Tie the Verified Person to the Commits?
This is the part I think engineering leaders skip. It’s ours to own. Nobody else will.
Identity verification is a point-in-time event. One moment. Somebody looked at a face and a document on a Tuesday. Your repo, though, trusts a credential every minute for six months. If the credential can move to a different person without anybody noticing, the Tuesday check bought you very little. Almost nothing. So the goal is to make the credential hard to hand off and easy to trace back to the person who was verified.
What that looks like in practice, roughly in the order I set it up:
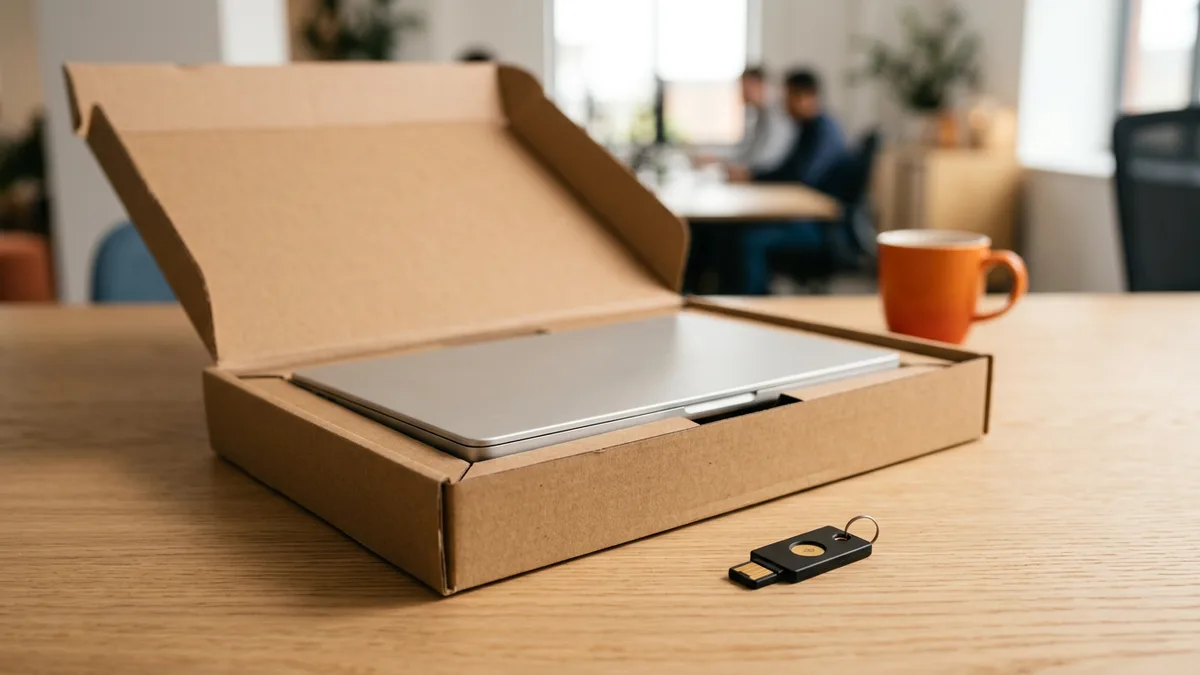
- A hardware security key ships in the same box as the laptop, to the ID address, and gets enrolled on a live video call with the same person you interviewed. That call is your second photo comparison.
- SSH and signing keys are created on the managed laptop and nowhere else. A key registered from a personal machine is a policy violation. Full stop.
- Signed commits on protected branches, with GitHub’s commit signature verification or your platform’s equivalent, so an unsigned commit under the contractor’s name stands out.
- One named account per human. No shared service logins for “the contract team.” Ever.
- Forking of private repositories to personal accounts turned off at the organization level, and third-party app access restricted. Remember the FBI’s line about copied repositories.
- Tokens that expire. Short-lived, scoped to the repos on the first ticket.
The scoping piece overlaps with how I think about SOC 2 access tiers for contract engineers, where the first ticket defines the first grant. That piece is about how much access. This one is about whose hands. You need both. They fail differently.
Under the hood, what you’re doing is moving the identity check from a single HR moment to something the repo can keep asking. The hardware key can’t be emailed to a laptop farm in another country. It can be mailed, I suppose. Nothing is perfect. But a physical object enrolled on camera is a lot more friction than a password and a push notification someone else approves.
Why Is a Recruiter Who Has Met the Person Part of the Control Set?
Devin Hornick, a partner at KORE1, said it in a line I keep repeating to CTOs: “A recruiter who actually knows the candidate is now a security control, not overhead.”
I agree with him. For a narrow reason, though. The FBI’s advice to photograph people and compare them later only works if somebody keeps comparing. A recruiter who spoke with the candidate before submission, again before the offer, and again in week two has seen that face and heard that voice across time, and continuity is exactly what a proxy scheme struggles with. Your hiring manager met the person once. Maybe twice. The recruiter is often the only human in the chain with a before and after.
That doesn’t make the recruiter your control owner. You are. It makes them a witness you should be asking. “Is this the same person you placed?” is a fair question in week two. Ask it. A good firm will take it seriously instead of getting defensive.
Hire remote contract engineers a recruiter has actually met
Tell KORE1 the roles, whether the seat is remote or onsite, your compliance regime, and your start date at contract engineering teams. Filling one seat where an auditor will look at the commits? See regulated industry software engineers.
What Should You Watch in the First Week?
Verification before access catches the lazy attempts. The first week catches the rest, if you’re looking. Here’s what I check, and where it shows up.
| Signal | Where you see it | What I do |
|---|---|---|
| Logins from several IP addresses or a VPN exit far from the claimed location | Identity provider and repo audit log | Ask on a live call, camera on |
| Remote desktop or screen-sharing software on the managed laptop | Endpoint management | Suspend access first, then talk |
| Clones or bulk pulls of repositories the first ticket doesn’t touch | Repo audit log | Tighten scope and ask why |
| Commit and chat activity in a time zone that doesn’t fit the claimed home | Commit timestamps, chat presence | Note it, and look for a second signal |
| Camera suddenly broken for stand-ups after a camera-on interview | Your own meetings | Fix it this week, not next |
| A request to change the payment account or shipping address | Staffing firm or HR | Re-verify identity before approving |
Nearly all of that table comes straight from the FBI and Okta lists, translated into the systems an engineering org already runs. The FBI’s January advisory tells employers to monitor for multiple logins from varied IPs, unauthorized remote desktop tools, and data moving to private repositories. Okta tells you to cross-check locations against IP data and time zones and to watch for unusual data pulls. GitHub’s organization audit log will show you clones, forks, and key changes if you look at it, which, honestly, most teams don’t until something has already gone wrong.
One caution. Signals aren’t verdicts. None of these proves fraud alone. A contractor in Denver who codes at two in the morning is a night owl, not a spy. I look for two signals that agree, and I’d rather have an awkward conversation on day four than a forensics engagement in month three.
There’s a softer signal too. The person in the stand-up should be the person from the interview. Same voice, same way of explaining a tradeoff, same gaps. If the engineer who struggled to explain a retry policy on Tuesday is writing flawless concurrency code on Thursday, I’m happy. Then I’m curious. Then I ask them to walk me through it on camera.
What Breaks If a Fake Contractor Gets Repo Access?
More than the repo. Much more.
The obvious loss is the code itself. The FBI has already told you the playbook, which is to copy the repositories to a personal account, wait, and ransom them back or release them. In a regulated shop, the code is rarely the worst of it. Repositories carry years of history, and history carries things people meant to delete, like a service credential committed in 2021 and “removed” in the next commit, still sitting in the log for anyone who clones. CI workflows hold secrets that deploy to environments the contractor was never granted. A single merged change to a pipeline file can read those secrets on the next run. Dependency changes slip through review when they look like routine version bumps.
Then the second-order costs. Every secret the account could reach gets rotated. Every merge it made gets re-reviewed. Every one. Your auditors want a timeline, and a customer under GLBA or a state privacy law may need a notice. If the DOJ’s California case is any guide, export-controlled technical data is on the table for defense and hardware companies too.
This is the part of the problem Devin flagged as the cybersecurity priority, the work that can’t wait until 2027, and I agree. When I scope the cleanup labor, these are the two seats I end up pricing, the engineer who re-reviews the code and the security engineer who runs the rotation and the timeline. Here’s what they bill on contract in the KORE1 Contract Rate Index 2026-Q4, effective October 16, 2026.
| Role (all levels) | Source | n | Bill rate p25 to p75 | Median | 3 months at median |
|---|---|---|---|---|---|
| Security analyst / engineer | KORE1 observed, primarily Southern California | 7 | $70 to $124/hr | $82/hr | $42,900 |
| Software engineer / developer | KORE1 observed, primarily Southern California | 16 | $91 to $120/hr | $105/hr | $54,600 |
Both cells come from KORE1 W2 contract placements started 2023 to 2026, at least five per cell, with the sample size stated. The contract rate methodology explains how observed and modeled cells differ. A small n means a wide band, and the security cell’s spread from $70 to $124 is a good example, so price your own seat before you budget off a median.
About $97,500 for a quarter of cleanup on two seats is not a catastrophe. It’s also money you spent because one check didn’t happen on a Tuesday. And it doesn’t count the week your senior engineers spent in war rooms instead of shipping, which is the cost that never shows up on an invoice.
KnowBe4’s story ends better than most, and the reason is worth copying. When the laptop arrived, the new hire started loading malware almost immediately. Its endpoint detection software alerted the security operations center at 9:55 p.m. Eastern, and the device was contained at about 10:20, roughly 25 minutes later, after the new hire told the SOC he was troubleshooting a speed issue and then stopped answering. No data was lost, KnowBe4 says, partly because new employees start in a highly restricted area with no access to production systems. The identity check failed. The access design held.
One incident, both lessons. Verify hard, and build as if you’ll occasionally get it wrong. When the contract ends, the same discipline runs in reverse, and the contractor access checklist covers revocation step by step.
How KORE1 Sources, Vets, and Places the Engineers This Model Assumes
This section is written by KORE1, not by Kris. Kris wrote the operating model above, and KORE1 supplies engineers who work inside it.
The model above assumes a contractor who was met by a real person before the offer and stays in contact with that person after the start. Our recruiters specialize by discipline, and every candidate is technically screened and reference-checked against the project before you see a resume. You can read how KORE1 vets candidates before you see a resume, and the supplier-side questions to put to any firm are on our remote contractor identity verification page.
Across KORE1 placements, IT roles take an average of 17 days to hire, contract offers reach a first day in a median of 3 days (n=1,997), and twelve-month retention is 92 percent. Contractors are KORE1 W-2 employees, paid weekly on Fridays, and any of them can move to your payroll at no fee after 1,040 hours.
One limit, stated plainly. No screening process makes identity fraud impossible, ours included, and our checks don’t replace yours. What any partner should give you is a recruiter who will answer “is this the same person?” honestly, a same-day notice when start or end dates change, and straight answers about how identity was confirmed.
What Engineering Leaders Ask Before Issuing Credentials
Is a clean background check proof the contractor is who they say they are?
No, because a background check confirms that an identity exists and is clean, not that the person on your video call owns it.
KnowBe4’s hire cleared a background check on a stolen identity. Treat the check as one input, and do the live video, document, and address matching on top of it.
The contractor came through a staffing firm. Do we still verify on our side?
Yes, at least once on your side, since the FBI tells employers to verify identity throughout hiring and employment and to audit the third-party staffing firms that supply contract IT workers.
The firm’s checks are useful. They’re also not yours. Different owner. The cheapest version I know is that the hardware key enrollment call becomes your verification moment, with the same camera rules as the interview and a quick comparison against the interview photo. Ask the firm, in writing, what it checked, when it checked it, and who on its side actually saw the candidate on camera, then keep that email with the onboarding record. If the answer is vague, that tells you something about the next six months.
Can a face-swap really get through a live video call?
The FBI says North Korean IT workers have used AI and face-swapping technology during video job interviews to hide who they are.
It didn’t say most, and I won’t either. Its July 2025 guidance gives you cheap counters, like cameras on with no background filter, a look around the room, and a hand waved in front of the face.
What’s the one repo setting I should change this week?
Turn off forking of private repositories to personal accounts, because copying company repositories to their own profiles is exactly what the FBI says these workers have done.
Then pull your organization audit log and look at who cloned what in the last 30 days. It takes an hour. Maybe less. I’ve never once done it and found nothing worth a follow-up question, though usually the answer is boring, an old automation token or someone’s forgotten laptop, and boring is fine. Boring is the goal.
Ask Whose Hand Is on the Key
The access review question I ask now is different from the one I asked five years ago. I used to ask whether the account had MFA. Easy question. Now I ask whose hand is on the key, and how we’d know if it changed.
If you can answer that for every contractor with write access, you’re in better shape than most of the shops I’ve seen. If you can’t, don’t panic. Start with the next one you onboard. Six checks before credentials, a key enrolled on camera, two signals before you raise an alarm.
If you’ve caught one of these in your own pipeline, I’d like to hear what tipped you off. Connect with me on LinkedIn. And if you have a remote seat to fill on a codebase that matters, talk to a KORE1 recruiter about who will actually meet the person.